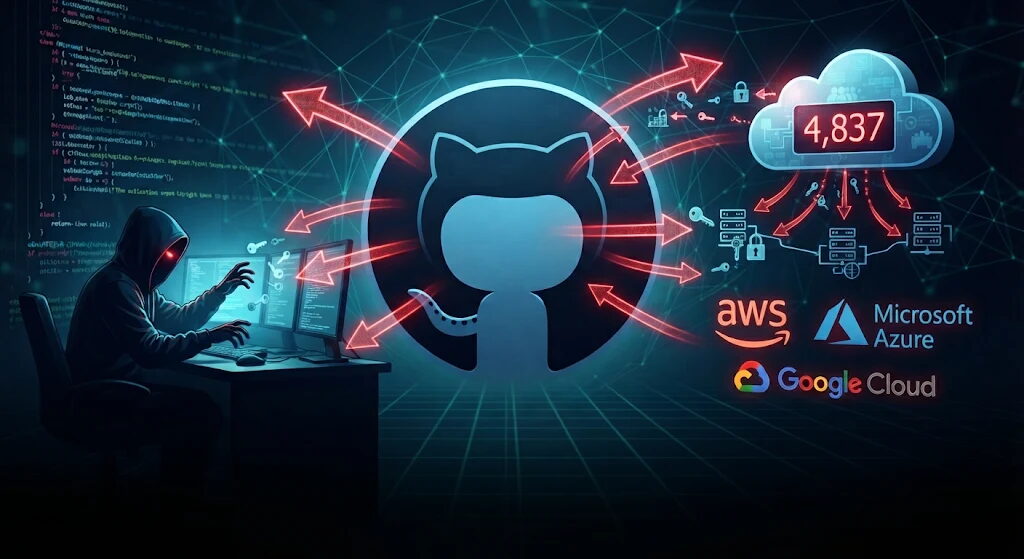
A large attack has hit GitHub. Security firm Aikido Security detected a campaign called wfx-loot from 10 November 2026, in which hackers used 4,837 GitHub accounts with stolen sign-in details to test access to as many as 61,764 code repositories. Evidence shows the malicious code was run in at least 1,800 of them.
The attack starts with a stolen account opening a pull request that looks like a routine check. If the account has permission to change code, the hackers try to slip a malicious script into GitHub Actions, the system developers use to test and build software automatically.
When the workflow runs, the script tries to steal any secrets the system can reach, such as tokens, API keys or credentials for cloud services like AWS, Microsoft Azure and Google Cloud, as well as keys for some AI services. Depending on the permissions set, these could let attackers into other systems in the organisation.
Worryingly, after the script runs, the hackers quickly revert the code change and delete the GitHub Actions run history, in many cases within about a minute. When project owners check later, they may find no trace of foreign code, even though important data may already have been sent out.
Researchers also found that the malware may try to keep access to cloud systems even after owners change the original keys. Some malicious code also ended up in software packages published through automated pipelines, adding risk for anyone who uses them.
Developers and organisations using GitHub should look for a pull request named “docs: dependency audit notes” or a branch named “wfx-docs”, as well as changes to GitHub Actions files and run history that has disappeared unexpectedly.
If the malicious script ran, immediately revoke the stolen credentials, rotate any keys that may have leaked, and check cloud permissions for any unknown access left behind.
This does not mean all of GitHub was hacked. The attack used stolen accounts and permissions to target individual projects, which can still cause knock-on damage.
Source: Notebookspec